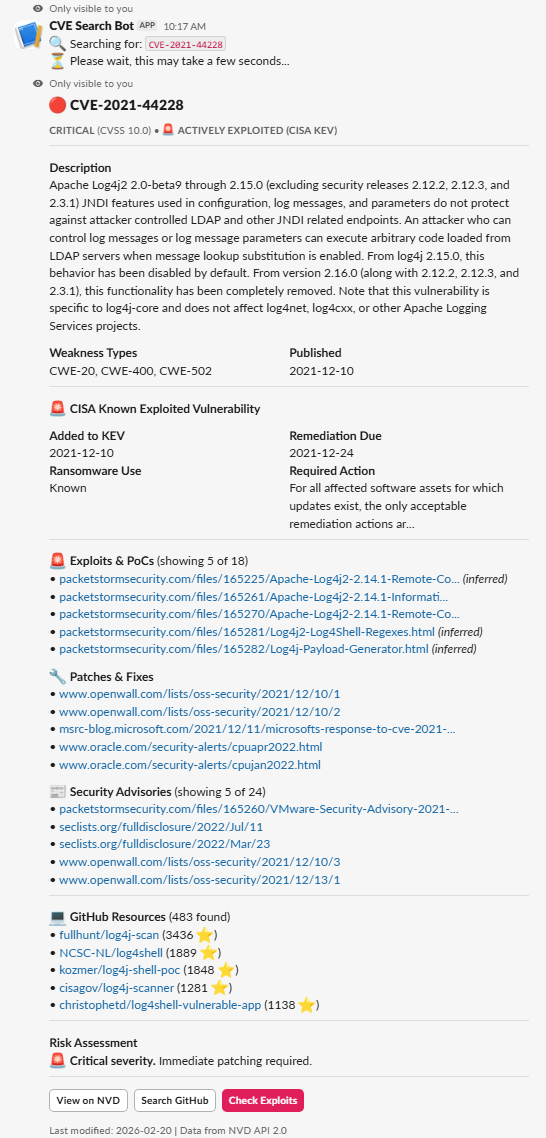
CVE Research Bot.
A Slack bot for researching CVEs with MCP-powered tool integration.
- Dates
- November 2025
Selected work
- Built a Slack bot with a separate MCP server for live CVE lookups, using httpx timeouts to bound API requests.
- Queued vulnerability research in Redis so workers could process it outside Slack request handling.
- Added URL-based rules to distinguish exploit references, patches, and advisories when NVD tags are missing.
- Configured a read-only filesystem for the MCP server container and an internal Docker network for Redis.
Built with
Python · Redis · Docker · Slack · httpx · MCP
Screenshots